Tech Support : support@safience.io

Blog

Middle school teacher arrested on child pornography charges

By a Biometrica staffer

A middle school teacher from Fontana, California, was arrested on child pornography charges by special agents with US Immigration and Customs Enforcement’s (ICE) Homeland Security Investigations (HSI).

Josue Gamaliel Vidal Quintanilla, 28, who teaches mathematics at Shandin Hills Middle School in San Bernardino, was charged for allegedly uploading explicit images to the internet. He was arrested on Wednesday after he admitted using various online platforms to send, receive and possess child pornography.

Evidence obtained by HSI agents and officers with the Fontana Police Department’s Internet Crimes Against Children Task Force indicates that Vidal used Kik Messenger and Snapchat for the past year to transmit child pornography.

He also posed as a minor boy on the internet and solicited “many” minors – some as young as 10 years old, according to the affidavit in support of the complaint. He solicited them to engage in sexually explicit behavior in online meetings, which took place as recently as Tuesday night.

“A preliminary search of Vidal’s Toshiba laptop revealed approximately 20 image files depicting the sexual exploitation of children, as well as multiple video files with titles indicative of child pornography,” according to the affidavit by an HSI special agent.

Vidal has been charged with one count of transportation of child pornography and one count of possession of child pornography. If convicted of both, he faces a statutory maximum sentence of 40 years in federal prison. Additionally, the transportation count carries a mandatory minimum penalty of five years in federal prison.

Michigan man pleads guilty to hate crime charges

By a Biometrica staffer

Ronald Wyatt, 22, pleaded guilty to intentionally threatening physical harm to a female victim, and to obstructing her religious freedom. Wyatt admitted that he targeted his African-American victim because of her race in his plea agreement, the US Department of Justice said in a statement.

Wyatt admitted that on July 23 2019 he used Facebook to send the victim – whom the DoJ identifies only by her initials (T.P.) – a threatening written message. The message read: “See you at church on Wednesday night with my AK to put you and your [expletive] family down [expletive].” T.P. regularly attends a church in Taylor, Michigan.

The perpetrator, a resident of Michigan, also admitted he acted intentionally to obstruct T.P.’s free exercise of her religious beliefs by sending the message. He said he threatened T.P. because she is African-American, and intended her to understand his message as a threat.

Mr. Wyatt used threats of violence to terrorize an innocent woman and as a result hindered the victim’s ability to freely practice her religion. Hate crimes like this one have profound effects not only on the victims, but also on their families and communities, making them feel vulnerable and unsafe. No arrest or conviction can undo the harm, but will hopefully provide a measure of justice for the victim, her family and her community.

Special Agent in Charge Steven M. D’Antuono, of the FBI’s Detroit Field Office

Wyatt’s sentencing will take place in a year, pursuant to the plea agreement. He faces a maximum sentence of one year in prison.

The defendant’s actions in this case are truly reprehensible. Although the First Amendment protects free speech, it doesn’t give anyone the right to obstruct the free exercise of religious beliefs by threatening violence or bodily harm. Prosecuting those who violate the civil rights of Michigan citizens is some of the most important work we do. This plea today is the first step towards justice for this innocent victim.

U.S. Attorney Matthew Schneider of the Eastern District of Michigan

ICE part of international crackdown on darknet drug dealers

By a Biometrica staffer

The US Immigration and Customs Enforcement’s (ICE) Homeland Security Investigations (HSI) and other agencies were part of an international operation to disrupt drug trafficking on the darknet. As part of the investigation, charges were also brought on against a key member of a Southern California drug trafficking organization, the ICE said in a statement.

The Southern California drug trafficking organization member allegedly distributed methamphetamine and other illicit narcotics to thousands of customers in at least 35 states and numerous countries around the world.

Andres Bermudez of Palmdale, who allegedly supplied methamphetamine to the “Stealthgod” crew, was named in a criminal complaint filed on September 18. An affidavit in this case outlines how Bermudez allegedly supplied methamphetamine to the “Stealthgod” drug trafficking organization, and details negotiations involving transactions of 30 and 40 pounds of methamphetamine.

Bermudez, 37, is currently a fugitive sought by federal authorities. Earlier this year, five other members of the narcotics ring were arrested on federal charges, and authorities made substantial seizures of narcotics and cryptocurrency.

Along with the HIS special agents, members of the Los Angeles Joint Criminal Opioid and Darknet Enforcement (JCODE) Task Force were also part of the team that brought charges against the Southern Californian drug dealer.

This case is a part of Operation DisrupTor, building on the success of prior actions targeting darknet vendors including the takedown of Wall Street Market, which was one of the world’s largest dark web marketplaces. Adter the Wall Street Market takedown in May 2019, and the filing of federal charges in Los Angeles against the administrators, law enforcement in the US and Europe obtained intelligence that allowed them to identify darknet drug traffickers.

During Operation DisrupTor, the Los Angeles JCODE Task Force successfully dismantled a drug trafficking organization that used online monikers such as “Stealthgod” to sell methamphetamine and MDMA (or ecstasy) on multiple darknet marketplaces, including Wall Street Market. Investigators have linked the crew to more than 18,000 illicit drug sales to customers around the world.

Earlier this year, members of JCODE executed search warrants that led to the seizure of more than 60 parcels containing narcotics that were ready to be shipped to more than 35 states around the nation.

Members of JCODE arrested five defendants allegedly at the center of the “Stealthgod” organization and seized roughly 120 pounds of methamphetamine, seven kilograms of MDMA and five firearms during law enforcement actions in the City of Los Angeles in February.

Texas woman part of heroin distribution conspiracy

By a Biometrica staffer

Cristina Godinez of San Antonio admitted to her role in a conspiracy to distribute heroin, after an investigation conducted by the US Immigration and Customs Enforcement’s (ICE) Homeland Security Investigations (HSI) and several other federal agencies.

Godinez, 36, pleaded guilty by videoconference before to an information charging her with one count of conspiracy to distribute, and possess with intent to distribute one kilogram or more of heroin. A co-defendant in the case – 43-year-old Alba Lilia Diaz of Chicago – also pleaded guilty to similar charges, the ICE said in a statement.

On July 22 2019, Diaz travelled to New Jersey to conduct a heroin sale, according to documents filed in this case and statements made in court. She provided a sample of heroin and agreed to deliver 15 kilograms several days later. On July 25 2019, Diaz and Godinez drove to New Jersey from Chicago with the heroin in their vehicle. When they arrived in New Jersey, Godinez negotiated the sale while Diaz waited with the drugs in a hotel room. Once a price was agreed on, Diaz brought the heroin to the buyer’s car. Special agents from HSI arrested the defendants and seized the drugs.

The conspiracy counts to which the defendants pleaded guilty carry a mandatory minimum term of 10 years in prison, a maximum of life in prison and a fine of $10 million, or twice the gross gain or loss caused by the offense. Sentencing for Godinez is scheduled for January 19 2021, and on November 20 this year for Diaz.

Along with HSI, the investigation was conducted by the Drug Enforcement Administration, the New Jersey State Police, the Camden County Prosecutor’s Office, and the Gloucester County High Intensity Drug Trafficking Area Task Force.

Man solicited murder, necrophilia, cannibalism of minor

By a Biometrica staffer

Alexander Nathan Barter, a resident of Joaquin, Texas, was sentenced to 40 years in federal prison on Thursday for child exploitation violations after he solicited the murder, necrophilia, and cannibalism of a minor on the dark web. Undercover special agents from the US Immigration and Customs Enforcement (ICE) were able to intercept the man and arrest him before he could carry out the heinous plot, the ICE said in a statement.

Barter was also ordered to submit to a lifetime of supervised release for attempted coercion and enticement of a minor and distribution of child pornography by District Judge Michael Truncale. He pleaded guilty to the charges. As part of his plea agreement, he agreed to be sentenced to imprisonment of 20 years on each count, with each party reserving the right to request that the terms be sentenced concurrently or consecutively.

In October 2018, Barter posted an ad on a dark web site stating: “I’d like to try necrophilia and cannibalism, and see how it feels to take a life. If you’d be willing to let me kill you, are in the U.S. (preferably in the south) and can travel by car, contact me.” An undercover special agent from ICE Homeland Security Investigations (HSI) saw the ad and responded, using the persona of a father with a 13-year-old daughter.

Between October 9 and 19 of that year, Barter and the undercover special agent exchanged a series of messages that included the latter’s repeated interest in killing, raping and eating the 13-year-old child. He provided the undercover with instructions on traveling from Florida to Shelby County, Texas, what to tell the child to get her to agree to travel, and how to conceal evidence of their crime. On October 19, Barter arrived at the designated site with a knife, trash bag, cellular phone and a tablet.

“As this chilling case demonstrates, online talk is not always just talk. The constant vigilance of our law enforcement partners has prevented an evildoer from finding a likeminded accomplice and bringing his grisly plan to fruition. This case is a sobering reminder of how the brave men and women of law enforcement face down the worst of the worst in the scariest of scenarios.”

Attorney Stephen J. Cox

The case is being investigated by HSI Beaumont; HSI Cocoa Beach; Florida Child Exploitation Task Force; Brevard County (Florida) Sheriff’s Office; Nacogdoches (Texas) Police Department; Texas Department of Public Safety; Customs and Border Protection Air Units; and Shelby County (Texas) Sheriff’s Office.

US launches coordinated effort to deter malicious cyber activities

By a Biometrica staffer

Four federal agencies launched a coordinated effort to disrupt and deter Iranian malicious cyber activities targeting the US and the broader international community, the Department of Justice (DoJ) said in a statement.

The DoJ, the Federal Bureau of Investigation (FBI), the Department of Homeland Security (DHS), and the Department of the Treasury (USDT) have been engaged in a coordinated effort since September 14 2020, which continued through September 17 2020.

The malicious cyber activities are said to have been conducted by actors associated with the Islamic Republic of Iran’s (Iran) Ministry of Intelligence and Security (MOIS) and Islamic Revolutionary Guard Corps (IRGC), as well as other Iran-based individuals. They targeted victims in Australia, Europe, the Middle East, Southeast Asia, and the US.

Timeline of events:

– On September 14 2020, the FBI and the DHS’ Cybersecurity and Infrastructure Security Agency jointly published a Cybersecurity Advisory regarding tactics, techniques, and procedures (TTPs) of an Iran-based malicious cyber actor targeting several US federal agencies and other US-based networks.

– On September 15 2020, the DoJ announced the unsealing of a three-count indictment in the District of Massachusetts charging two hackers in relation to their intrusions into, and defacements of, websites hosted in the US. The hackers were Behzad Mohammadzadeh (aka “Mrb3hz4d”) – a citizen and resident of Iran – and Marwan Abusrour (aka “Mrwn007”) – a stateless national under the jurisdiction of the Palestinian Authority.

They allegedly conspired to and subsequently damaged computers in what is perceived as retaliation for the US military strike that killed Qasem Soleimani, the head of the IRGC-Quds Force on January 2 2020. The IRGC-Quds Force is a branch of the IRGC, and a US-designated Foreign Terrorist Organization. The website defacements were a subset of the over 1,400 defacements around the world, for which the defendants claimed responsibility, between roughly June 2016 and July 2020.

(Website defacement involves malicious attacks wherein the hacking party replaces the original content of a website with its own message.)

– On September 16 2020 in the District of New Jersey, the DoJ announced the unsealing of a 10-count indictment charging two hackers, who sometimes operated under the pseudonym “Sejeal,” in relation to coordinated cyber intrusions and hacking campaigns targeting computer systems in Europe, the Middle East, and the US. The defendants, Hooman Heidarian (aka “neo”) and Medhi Farhadi (aka “Mehdi Mahdavi”) – both Iranian nationals residing in Iran – stole hundreds of terabytes of data, which typically included confidential communications pertaining to national security, foreign policy intelligence, non-military nuclear information, aerospace data, human rights activist information, victim financial information and personally identifiable information, and intellectual property, including unpublished scientific research.

In some instances, the defendants’ hacks were politically motivated or at the behest of the government of Iran, including instances where they obtained information regarding dissidents, human rights activists, and opposition leaders. In other instances, the defendants sold the hacked data and information on the black market for private financial gain.

– On September 17 2020, the Department announced the unsealing of a nine-count indictment charging three hackers in relation to a near four-year campaign to steal, and attempt to steal, critical information related to aerospace and satellite technology and resources, including sensitive commercial information, intellectual property, and personal data. The defendants, Said Pourkarim Arabi, Mohammad Reza Espargham, and Mohammad Bayati – all Iranian nationals residing in Iran – conducted their activity at the direction of the IRGC, of which Arabi was a member.

The defendants primarily accomplished their intrusions through socially engineered spearphishing campaigns, using at least one target list of over 1,800 individuals in Australia, Israel, Singapore, the US, and the UK. Upon successfully enticing a victim to click on a link in a spearphishing mail, a member of the conspiracy would deploy malware that allowed the conspirators to gain access credentials, escalate their privileges, maintain their unauthorized access to victim networks, and ultimately steal the sought-after data. To accompany the unsealing of this indictment, and to aid potential targets in the identification of malicious activity, the FBI released a Private Industry Notification (PIN) that identified the conspiracy’s TTPs and indicators of compromise.

(Spearphishing is an email scam that is targeted at a specific person or organisation. It can either be intended to be used to steal data for malicious reasons, or to install malware on a targeted user’s system.)

– On September 17 2020, the Treasury Department’s Office of Foreign Assets Control (OFAC) imposed sanctions against 45 individuals and one front company associated with the Iranian MOIS. Together they made up the cyber threat group known publicly as “Advanced Persistent Threat 39” (APT39), “Chafer,” “Remexi,” “Cadelspy,” or “ITG07.” According to OFAC, masked behind its front company – Rana Intelligence Computing Company (Rana) – the MOIS employed a year-long malware campaign that targeted Iran’s own citizens, the government networks of Iran’s neighboring countries, and US-based travel services companies.

Concurrent with OFAC’s action, and following a long-term FBI investigation, the FBI released technical indicators about Rana’s malware in an FBI FLASH alert. This alert provides information to assist organizations and individuals in determining whether they were targeted by Rana.

Note – the details contained in the above-described charging document are allegations. The defendants are presumed innocent until proven guilty beyond a reasonable doubt in a court of law.

Kansas man indicted on child pornography charges

By a Biometrica staffer

A resident of Kansas has been indicted by a federal grand jury on federal child pornography charges, the US Department of Justice said in a statement.

The three-count indictment charged Jeffrey Pierce, who lives in Topeka, with producing and possessing child pornography. He also allegedly solicited sexually explicit images and videos from minor victims.

Pierce was indicted in the U.S. District Court for the District of Kansas, Acting Assistant Attorney General Brian Rabbitt of the Justice Department’s Criminal Division said.

No further details about Pierce’s case were given in the DoJ statement.

Graphic created by Biometrica

The case is part of Project Safe Childhood. Launched in May 2006 by the DoJ, Project Safe Childhood is a nationwide initiative to combat the growing epidemic of child sexual exploitation and abuse. Led by U.S. Attorneys’ Offices and the Criminal Division’s Child Exploitation and Obscenity Section, Project Safe Childhood marshals federal, state and local resources to better locate, apprehend and prosecute individuals who exploit children online, as well as to identify and rescue victims.

Las Vegas man sentenced 35 yrs for child sexual abuse

By a Biometrica staffer

A man was sentenced to 35 years in federal prison for repeatedly sexually assaulting a child, producing images of the sexual abuse, and possessing hundreds of images and videos of the sexual assaults.

Andres Rafael Viola, an Argentine citizen living in Las Vegas, pleaded guilty to charges of sexual exploitation of children and possession of child pornography in February. In addition to imprisonment, Viola was sentenced to a lifetime term of supervised release by District Judge Richard F. Boulware II, the US Immigration and Customs Enforcement (ICE) said in a statement.

Viola has to register as a sex offender under the Sex Offender Registration and Notification Act (SORNA). His sentence also includes a $10,000 assessment pursuant to the Justice of Victims of Trafficking Act.

The case was investigated by the ICE’s Homeland Security Investigations (HSI) and Sheriff Joseph Lombardo of the Las Vegas Metropolitan Police Department (LVMPD).

Safeguarding children from being victimized by predators is a top priority for ICE and Homeland Security Investigations. We are most appreciative of the collaborative partnership with the LVMPD – together, we will continue to scour our society of these aberrant people.

HSI Las Vegas Special Agent in Charge Francisco Burrola

In May 2019, the National Center for Missing and Exploited Children (NCMEC) received a report from Yahoo Inc that a user received child pornography sent by Viola, who was using the dark web Tor network to distribute images of child sexual assault.

On June 7, 2019, federal law enforcement arrested Viola at his Las Vegas residence. They determined that Viola had supervisory control over a child victim. A forensic examination of electronic devices that were seized from his home revealed nearly 350 child pornography images and video, including Viola’s sexual exploitation of the child victim and a curated collection of child pornography from other victims.

For the hands-on offenses related to the child victim, Viola pleaded guilty in Nevada state court to one count of sexual assault of a child under the age of 14.

Texas woman charged for $1.9 mln covid-relief fraud

By a Biometrica staffer

A Texan woman has been taken into custody on allegations of defrauding the Paycheck Protection Program (PPP) of more than $1.9 million in forgivable loans, the US Department of Justice said in a statement.

The Small Business Administration (SBA) guarantees PPP loans under the Coronavirus Aid, Relief and Economic Security (CARES) Act.

Lola Shalewa Barbara Kasali, 22, has been charged with making false statements to a financial institution, wire fraud, bank fraud and engaging in unlawful monetary transactions. The criminal complaint alleges Kasali submitted at least two fraudulent PPP loan applications.

One application was submitted on behalf of an entity called Lola’s Level and the other in the name of Charm Hair Extensions. Kasali allegedly received the amount after the Lola’s Level application was approved. After receiving the funds, she transferred the money into four additional bank accounts, the complaint further alleges. Authorities were able to seize the funds later, according to the charges.

The loan applications allegedly asserted both Charm Hair Extensions and Lola’s Level had numerous employees and significant payroll expenses. However, neither entity has employees nor pays wages consistent with the amounts claimed, according to the complaint.

PPP & the CARES Act

Established by the CARES Act, the PPP provides small businesses with necessary funds to remain operational despite the severe economic hit from the covid-19 pandemic.

The CARES Act is designed to provide emergency financial assistance to millions of Americans who are suffering the economic effects of the covid-19 pandemic, and was enacted as federal law on March 29. One source of relief is the authorization of up to $349 billion in forgivable loans to small businesses for job retention and certain other expenses through the PPP. In April, Congress authorized over $300 billion in additional PPP funding.

Through PPP, qualifying small businesses and other organizations are eligible to receive loans with a maturity of two years and an interest rate of 1%. Businesses must use PPP loan proceeds for payroll costs, interest on mortgages, rent and utilities. The PPP allows the interest and principal to be forgiven if businesses spend the proceeds on these expenses within a set time period, and use at least a certain percentage of the loan towards payroll expenses.

Anyone with information about allegations of attempted fraud involving COVID-19 can report it by calling the Department of Justice’s National Center for Disaster Fraud Hotline at 866-720-5721 or via the NCDF Web Complaint Form.

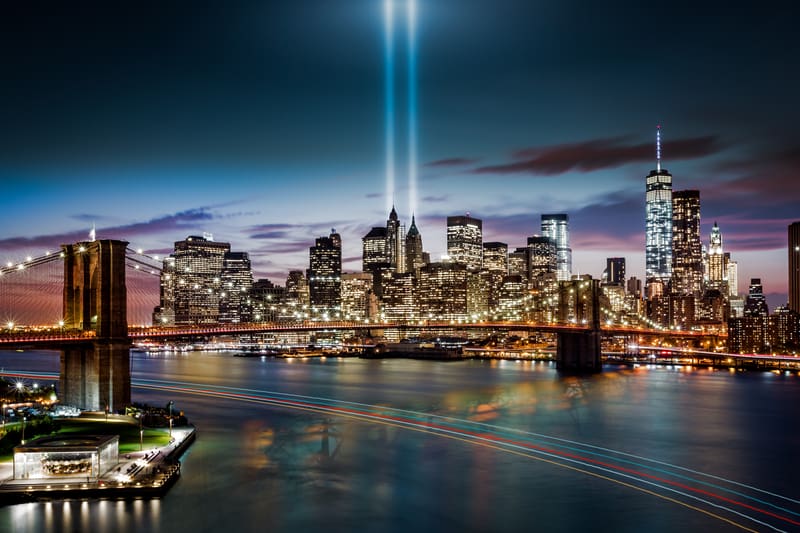
Never forget – September 11, 2001

Photo: © Mihai Andritoiu | Dreamstime.com

By a Biometrica staffer

It has been nineteen years since the deadliest terror attacks on American soil resulted in the deaths of nearly 3,000 people. The US Department of Justice paid a special tribute to the more than 70 members of its law enforcement family who lost their lives that day.

Here are snippets from the statements issued by Attorney General William P. Barr and Deputy Attorney General Jeffrey A. Rosen.

On behalf of the Department of Justice, I convey my sympathy to the families of the victims of all who were lost that tragic day. Although nearly two decades have passed, we will never forgot those who were murdered. Nor will we forget who murdered them. This department’s resolve to protect the people of the United States — and to bring to justice those who would harm them — is as strong as it was on September 12, 2001.

On this anniversary, I extend particular gratitude to the law enforcement personnel and others who responded courageously to the attacks, many of whom gave the last full measure of devotion to save others that day and many of whom have later suffered from illness related to the attacks. The deadliest day in the history of American law enforcement was also its finest hour. In the images of police officers and firefighters charging into the burning towers and carrying to safety victims from all walks of life, we see the true character of those who volunteer to protect and serve. All Americans owe them their gratitude and steadfast support.

Attorney General Barr

For the full text of the Attorney General’s statement, click here.

Here, at the Department of Justice, we pay special tribute to the more than 70 members of our law-enforcement family whom we lost that day.  We also remember the first-responders who sacrificed their health and safety at Ground Zero in the aftermath of the collapse of the Twin Towers — many of whom ultimately gave their lives.  

Inspired by their selflessness, we rededicate ourselves to the relentless pursuit of justice and security and to the common values that bind us as a Nation.

Now too, we must make common cause with our fellow citizens and unite to face a national challenge of a different sort:  the COVID-19 pandemic. For the first time in over 100 years, we face a public health crisis that reaches coast to coast and around the globe. But I am confident that our country, and the Department of Justice in particular, are up to the task.

Deputy Attorney General Rosen

For the full text of the Deputy Attorney General’s statement, click here.